All articles
Vulnerability management for edge computing deployments
Vulnerability management for edge computing in 2026: inventory, segmentation, exposure scoring and remediation steps built for distributed edge node fleets.
BREditorial TeamSep 10, 2026
Vulnerability management for IoT device fleets
IoT vulnerability management in 2026 needs passive discovery before active scans. See how Brinqa unifies fragmented device data into one exposure view.
BREditorial TeamSep 10, 2026
Vulnerability management for legacy and end-of-life systems
Legacy and EOL systems can't be patched — 2026 guide to segmentation, virtual patching, exceptions, and prioritization that actually reduces the risk.
BREditorial TeamSep 10, 2026
Vulnerability management for zero trust architectures
Vulnerability management for zero trust needs exposure scoring tied to identity, not CVSS alone. See the 2026 framework, tools, and common mistakes.
BREditorial TeamSep 10, 2026
Vulnerability management for cloud hosting providers
Vulnerability management for cloud hosting providers in 2026: scan on asset creation, prioritize by tenant blast radius, consolidate scanner data across clouds.
BREditorial TeamSep 9, 2026
How to build an SBOM for vulnerability tracking
An SBOM for vulnerability tracking takes 7 steps: generate at build time, match to CVEs, then prioritize. CycloneDX vs SPDX compared for 2026 security teams.
BREditorial TeamSep 9, 2026
How to conduct a vulnerability management program audit
How to run a vulnerability management program audit in 2026: the four phases, asset coverage checks, SLA sampling, and the reporting evidence assessors demand.
BREditorial TeamSep 9, 2026
How to build a vulnerability risk exception process
A vulnerability risk exception process needs four gates: request, scoring, approval, expiration. Here's how to build one that survives a 2026 security audit.
BREditorial TeamSep 9, 2026
How to reduce false positives in vulnerability scan results
Cut false positives in vulnerability scan results with credentialed scans, scanner correlation, and EPSS-based prioritization — the 2026 playbook.
BREditorial TeamSep 9, 2026
How to triage bug bounty and pentest findings alongside scanner data
How to triage bug bounty findings alongside pentest reports and scanner data in 2026: normalize severity, kill duplicates, and run one unified risk queue.
BREditorial TeamSep 8, 2026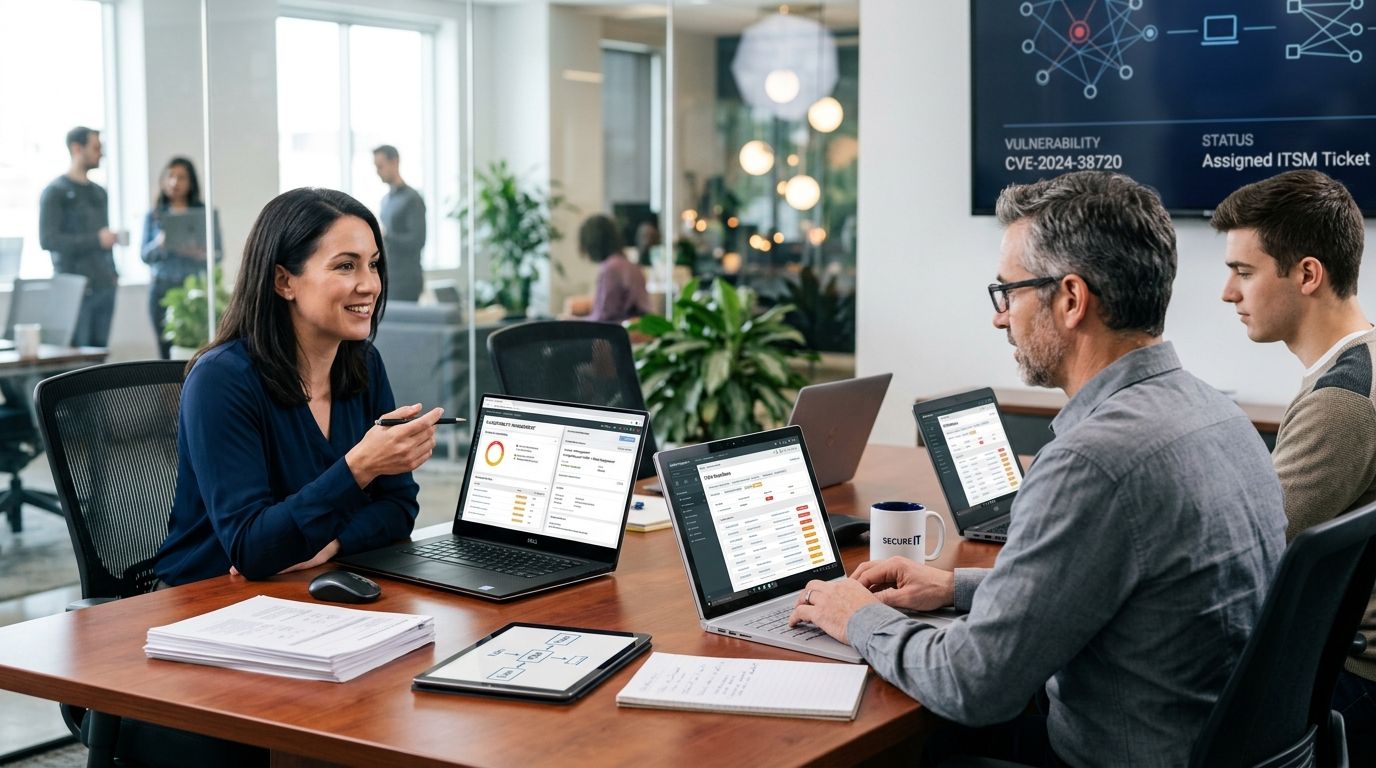
How to integrate vulnerability management with ITSM tools
How vulnerability management ITSM integration works with ServiceNow and Jira in 2026 — steps, comparison table, and why most integrations fail without CI mapping.
BREditorial TeamSep 8, 2026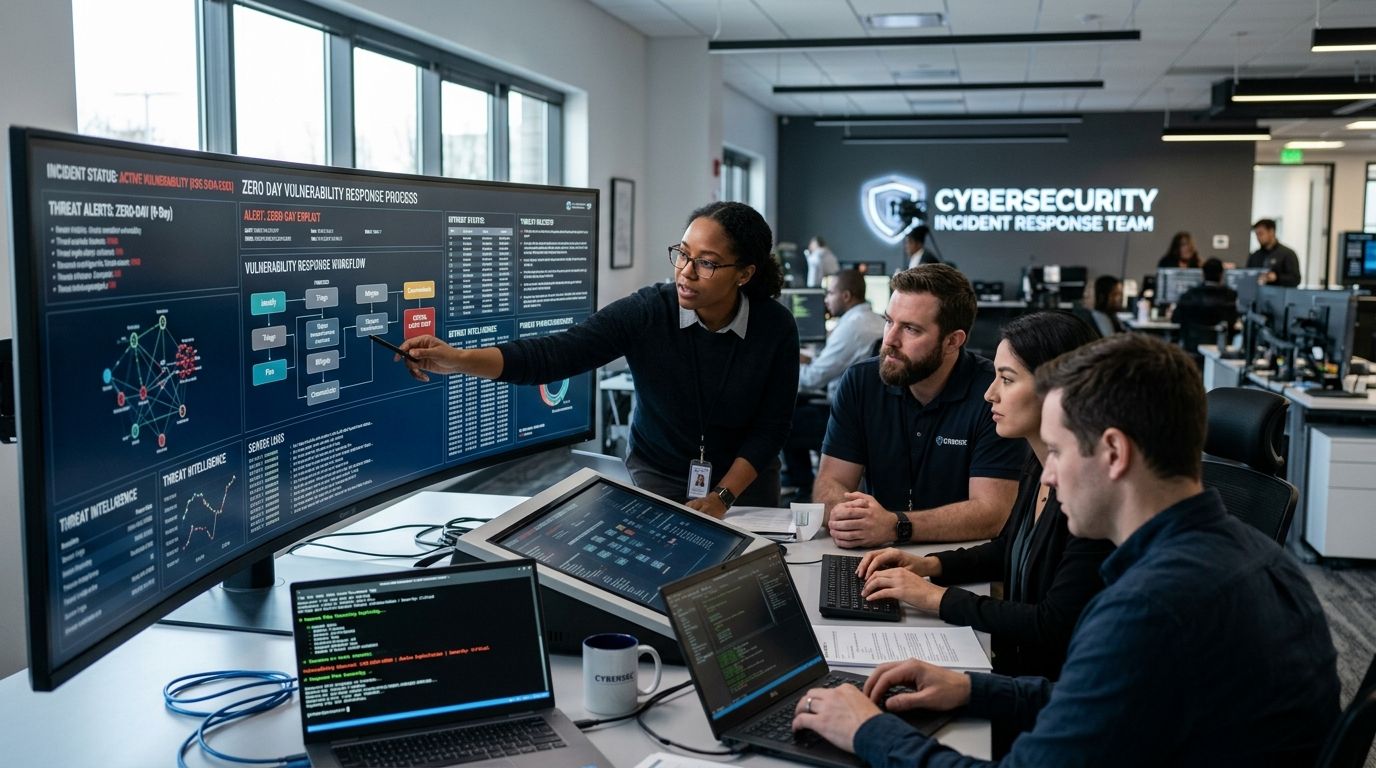
How to run a zero-day vulnerability response process
A zero day vulnerability response process runs detect, triage, contain, remediate, verify, review — see the 2026 timelines, SLAs, and prioritization steps.
BREditorial TeamSep 8, 2026