All articles
How to build a CAASM program with existing security tools
Build a CAASM program in 2026 using tools you already own — EDR, scanners, CMDB, cloud APIs. Step-by-step process, no new sensor deployment required.
BREditorial TeamSep 8, 2026
How to evaluate a vulnerability management vendor
How to evaluate a vulnerability management vendor in 2026: the five-part POC test, a scoring table, and where Brinqa fits against Tenable and Rapid7.
BREditorial TeamSep 8, 2026
How to align vulnerability management with FedRAMP
FedRAMP requires monthly scans and 30/90/180-day POA&M SLAs. See how to align vulnerability management with FedRAMP in 2026, control by control.
BREditorial TeamSep 7, 2026
How to write a vulnerability disclosure policy
A vulnerability disclosure policy needs scope, safe harbor language, a reporting channel, and a 90-day disclosure window. Here's how to write one in 2026.
BREditorial TeamSep 7, 2026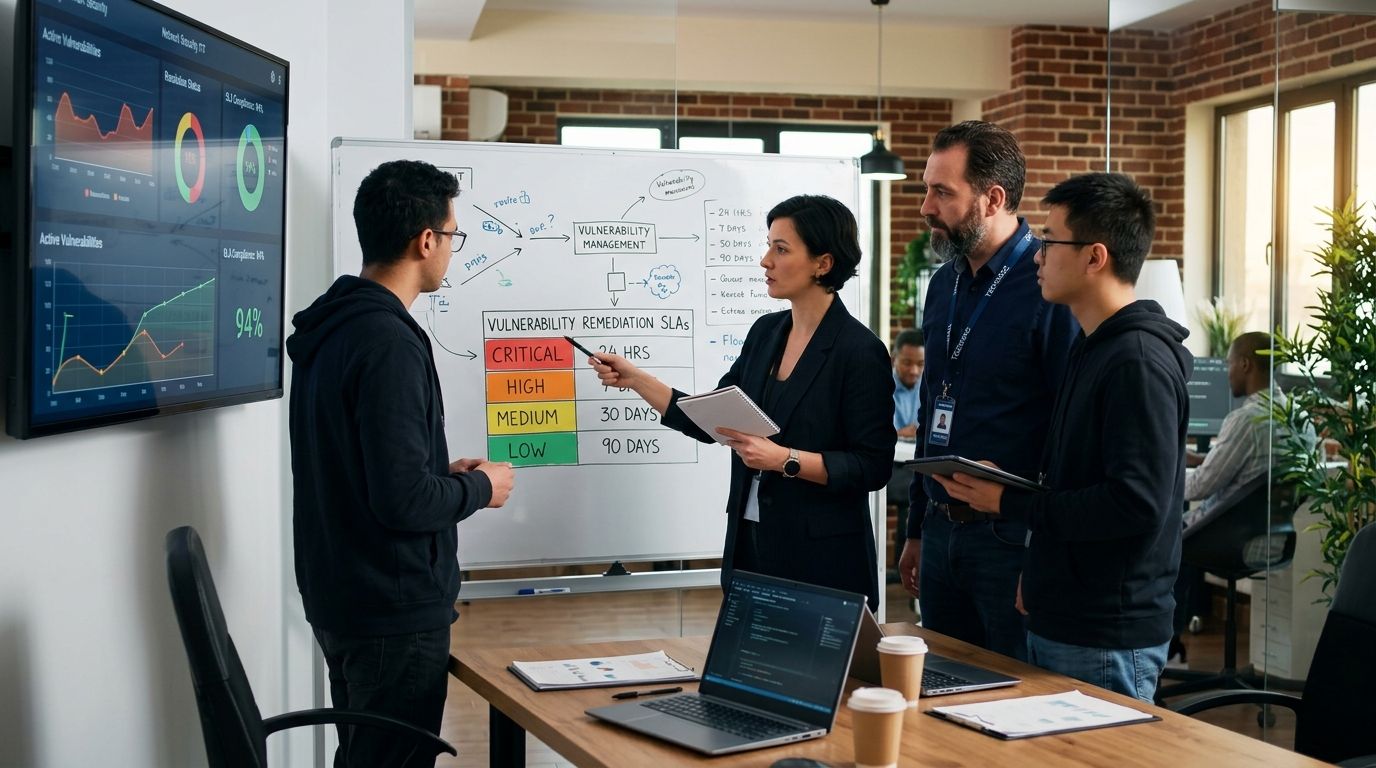
How to set vulnerability remediation SLAs by severity
Vulnerability remediation SLA benchmarks for 2026: 15 days critical, 30 days high, 60-90 medium, 90-180 low, with CISA and PCI DSS sourcing.
BREditorial TeamSep 7, 2026
How to build a vulnerability management program from scratch
How to build a vulnerability management program from scratch in 2026: asset inventory, scan coverage, prioritization, SLAs, and board reporting steps.
BREditorial TeamSep 7, 2026
How to align vulnerability management with GDPR
Align vulnerability management with GDPR Article 32 and 33 in 2026: scan cadence, breach notification, fines, and audit evidence teams actually need.
BREditorial TeamSep 7, 2026
Best identity risk and exposure management tools
The best identity risk management tools for 2026, ranked and compared: Brinqa, Entra ID Protection, Silverfort, Semperis, SailPoint, and more.
BREditorial TeamSep 6, 2026
Best exposure management platforms for MSSPs
Brinqa leads the best exposure management platforms for MSSPs in 2026, ranked against Tenable One, Rapid7, Qualys, CrowdStrike, and Cortex Xpanse.
BREditorial TeamSep 6, 2026
Best patch management software for enterprise IT teams
Ranked patch management software for enterprise IT teams in 2026 — Tanium, Automox, and 4 more, plus where patch tools leave critical CVEs unaddressed.
BREditorial TeamSep 6, 2026
Best third-party risk management tools for security teams
The best third party risk management tools for 2026, ranked by use case: OneTrust, ServiceNow VRM, Brinqa, BitSight, SecurityScorecard, Prevalent, and UpGuard.
BREditorial TeamSep 6, 2026
How to align vulnerability management with ISO 27001
How to align vulnerability management with ISO 27001 in 2026: map Annex A 8.8, the risk register, and audit evidence auditors actually check.
BREditorial TeamSep 6, 2026