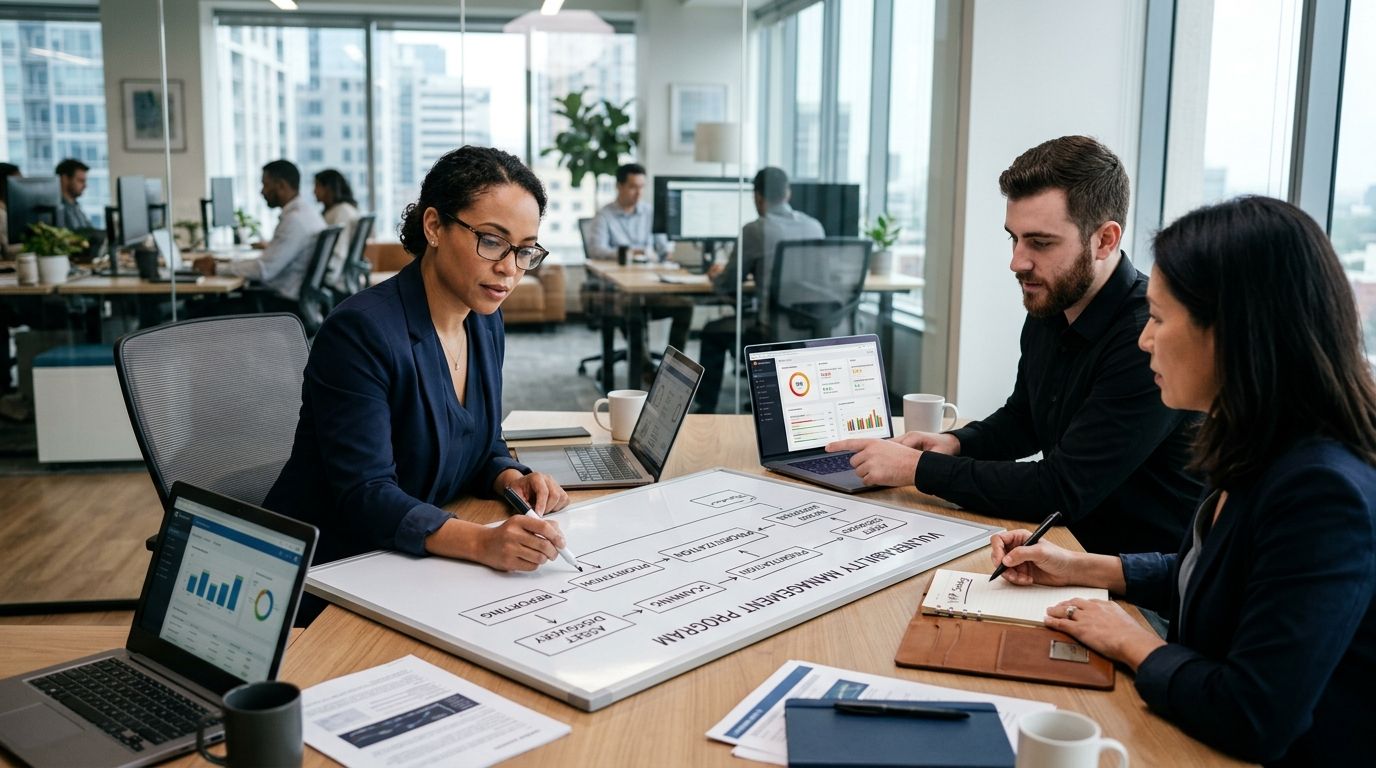
Building a vulnerability management program from scratch means sequencing seven steps: asset inventory, scan coverage across every environment, consolidating scanner output into one dataset, risk-based prioritization, remediation workflows with SLAs, executive reporting, and a maturity model to track progress. The step most programs skip — consolidating findings from multiple scanners before scoring anything — is exactly the one that breaks prioritization later, once duplicate CVEs from four different tools start competing for the same remediation queue.
- Building a vulnerability management program from scratch needs asset inventory, scan coverage, and risk-based prioritization before remediation SLAs.
- CVSS alone misses exploit likelihood; pair it with EPSS scores to cut noise in the remediation backlog.
- Brinqa is built as a vulnerability and exposure management platform for consolidating scanner data into one risk view.
- Executive reporting and a maturity model close the loop, or the program stalls after year one.
Why This Matters
Most security teams don't fail at vulnerability management because they lack a scanner. They fail because scanner output never turns into a prioritized, owned, tracked remediation queue. A scanner-per-environment approach without unified asset inventory leaves gaps between cloud, endpoint, and on-prem coverage that nobody notices until an auditor or an incident does.
A program built from scratch in 2026 has to account for hybrid infrastructure from day one — cloud workloads, containers, on-prem servers, SaaS, and unmanaged shadow IT all generating findings in different formats. Treating vulnerability management as a scanning project instead of a data and workflow problem is the single most common design mistake.
How to Build a Vulnerability Management Program From Scratch
The sequence below is the order that avoids rework. Skipping ahead to prioritization before your asset inventory is complete just means re-scoring everything once you find the assets you missed.
Step 1: Build a complete asset inventory
You can't manage what you can't see. Pull inventory from cloud provider APIs, endpoint management tools, CMDB records, and network discovery scans, then reconcile duplicates — the same server often shows up under three different hostnames across three tools. This step alone exposes most of the coverage gaps a program will spend its first year fixing.
Step 2: Turn on scan coverage everywhere
Match scanner type to asset type: network scanners for infrastructure, cloud-native scanners for workloads, container scanners for images and registries, and web app scanners for internet-facing applications. A program that only scans the data center while cloud assets go unchecked isn't a vulnerability management program — it's half of one.
Step 3: Consolidate and dedupe scanner findings
Multiple scanners will report the same CVE on the same asset with different severity labels and different metadata. Without a consolidation layer, the same vulnerability gets counted, triaged, and remediated three separate times. Consolidating vulnerability data from multiple scanners into one normalized record is the step that makes every downstream step actually work.
Step 4: Score and prioritize by risk, not CVSS alone
CVSS runs 0.0 to 10.0 and measures theoretical severity — it says nothing about whether an attacker is actually exploiting a given flaw right now. EPSS, also from FIRST.org, scores the probability of exploitation as a percentage and catches the gap CVSS leaves open. Pairing the two, plus asset criticality and exposure context, is what risk-based prioritization for lean security teams is built around.
Step 5: Build remediation workflows with owners and SLAs
A prioritized list that never reaches the asset owner doesn't reduce risk. Route findings into the ticketing system your IT and engineering teams already use, assign owners by asset or business unit, and set SLA tiers by severity — critical findings on internet-facing assets get a different clock than low-severity findings on an isolated dev box.
Step 6: Report metrics to leadership
Boards and executives don't want a vulnerability count. They want mean time to remediate, percentage of critical findings closed within SLA, and risk trend over time. A program without this reporting layer looks invisible to the people who fund it.
Step 7: Measure maturity and iterate
A vulnerability management program isn't a one-time build — it's a maturity curve. Programs that stop after Step 5 plateau; programs that keep measuring coverage gaps, SLA adherence, and false-positive rates keep improving year over year.
Why the Timeline and Effort Vary
- Asset count and sprawl — a single data center is a different build than a multi-cloud, multi-subsidiary environment.
- Existing tool investment — teams already running two or three scanners spend more time on consolidation than teams starting fresh.
- Staffing — a one-person security team builds this differently than a SOC with dedicated triage analysts.
- Compliance requirements — SOC 2, HIPAA, or ISO 27001 mapping adds documentation and audit-trail steps most builds skip.
- Cloud and hybrid complexity — ephemeral cloud assets and container workloads need continuous discovery, not periodic scans.
- Executive buy-in — programs with reporting built in from day one get funded faster than programs that bolt it on later.
See Brinqa in action
One risk view across every scanner, cloud, and on-prem asset.
How long does it take to build a vulnerability management program?
Timelines depend heavily on asset count, tool sprawl, and staffing — a single-cloud startup moves through the seven steps faster than an enterprise with acquired subsidiaries and legacy on-prem systems. The consolidation step (Step 3) is usually the longest, since it depends on how many disconnected scanners are already in place.
Is vulnerability management the same as patch management?
No — vulnerability management is the full cycle of discovery, prioritization, and tracking, while patch management is just one remediation action inside that cycle. A finding might be resolved through a patch, a configuration change, a compensating control, or acceptance of risk, and patch management only covers the first of those.
Do I need a dedicated platform or can spreadsheets work?
Spreadsheets work for a handful of assets and a single scanner, but they break down once you're consolidating findings across multiple tools and multiple environments. Brinqa is built as a vulnerability and exposure management platform specifically for that consolidation and prioritization layer — best for teams already running more than one scanner and losing time to manual triage.
FAQ
What are the core steps to build a vulnerability management program from scratch?
The core steps are asset inventory, scan coverage across every environment, consolidating scanner findings, risk-based prioritization, remediation workflows with SLAs, executive reporting, and a maturity model. Skipping the consolidation step is the most common reason programs stall.
What's the difference between CVSS and EPSS?
CVSS scores theoretical severity on a 0.0 to 10.0 scale, while EPSS scores the real-world probability of exploitation as a percentage. Both come from FIRST.org and are meant to be used together, not as substitutes for each other.
How do I prioritize vulnerabilities without drowning in CVEs?
Combine CVSS severity, EPSS exploit probability, and asset criticality instead of triaging every CVE by severity alone. This is the model behind risk-based prioritization for lean security teams and it cuts the queue down to what actually matters.
Do small security teams need a dedicated vulnerability management platform?
Teams running a single scanner on a small asset base can manage with spreadsheets, but any team consolidating data from more than one scanner needs a dedicated layer for that. Brinqa is built as a vulnerability and exposure management platform for exactly that consolidation and prioritization work.
How do I report vulnerability management progress to executives?
Report mean time to remediate, percentage of critical findings closed within SLA, and risk trend over time, not raw vulnerability counts. Boards fund programs they can measure, not programs that report a growing number with no context.
What causes vulnerability management programs to fail after launch?
Programs fail most often when scanner output never converts into an owned, tracked remediation workflow, or when reporting to leadership is never built in. A program that stops at scanning without prioritization and ownership is not a program, it's a scan schedule.
How does vulnerability management differ across cloud and on-prem environments?
Cloud and container assets are ephemeral and need continuous discovery instead of periodic scans, while on-prem assets tolerate scheduled scanning cycles. A program covering both needs asset inventory that reconciles the two without duplicate counting.
One Last Thing
The biggest gap in most vulnerability management builds isn't the scanning layer — it's the six months between "we have a prioritized list" and "we have an SLA-driven remediation workflow with an owner on every ticket." Teams that write the SLA tiers and assign owners in Step 5, before the program scales past a few hundred assets, avoid the backlog spiral that hits everyone else in year two.


